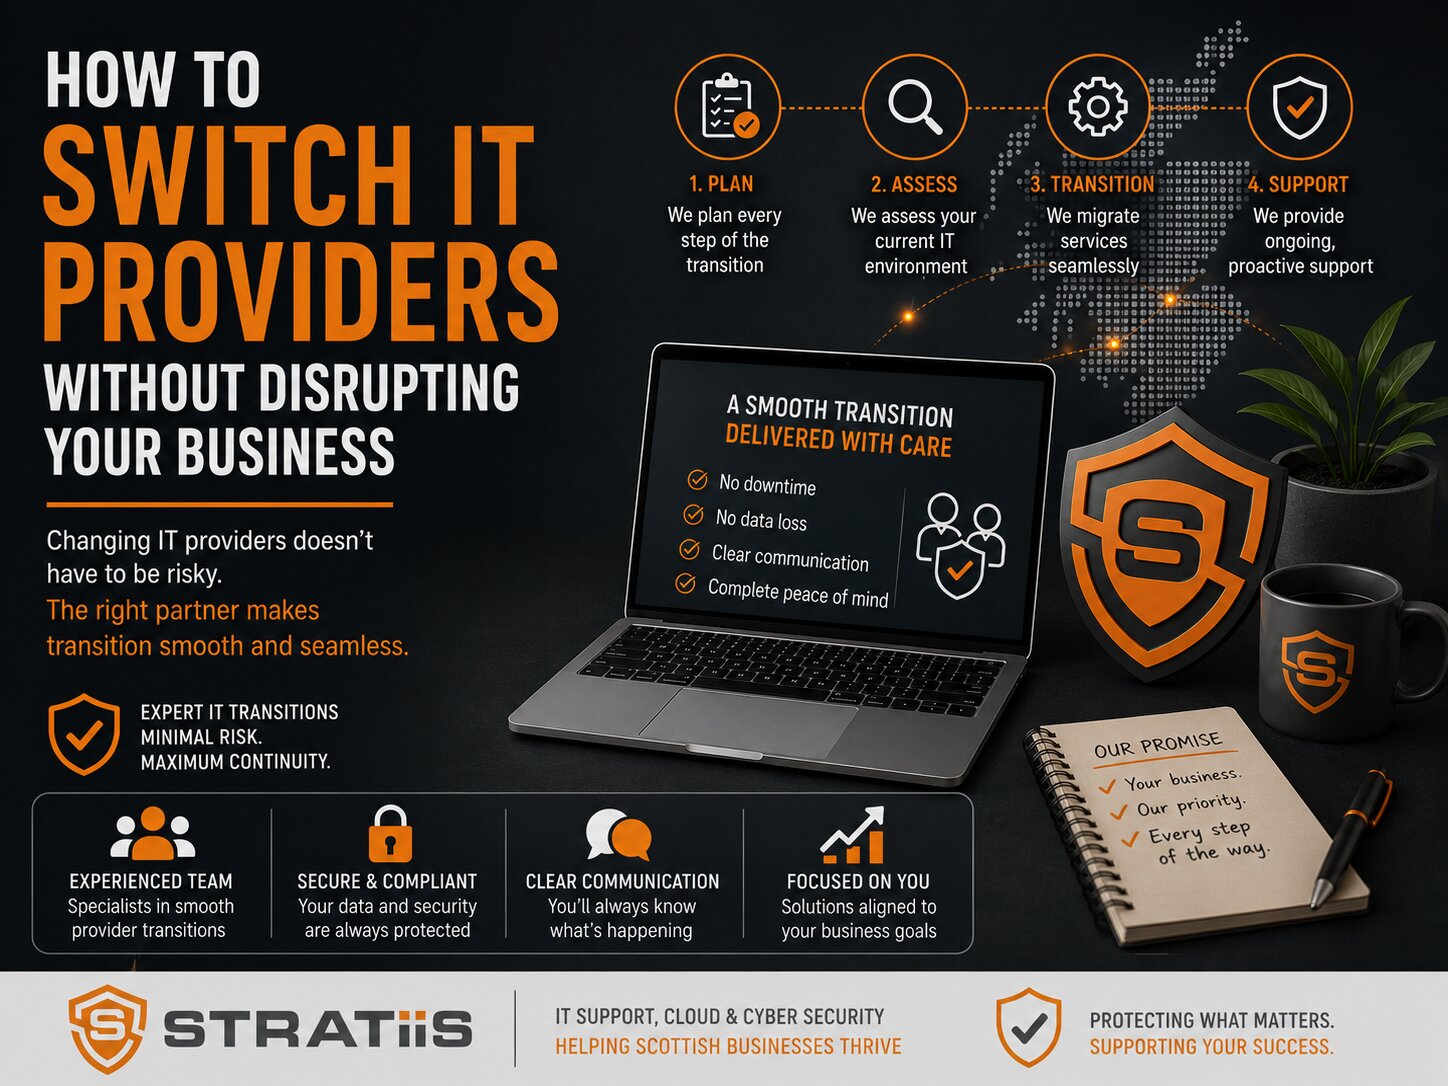
Switching IT providers does not need to cause downtime or confusion. A controlled change starts with clear responsibilities, secure access, reliable documentation and a plan for the first weeks of service. Most of the work can happen behind the scenes while employees continue using email, files and business systems.
The short answer
You can switch IT providers with minimal disruption when the incoming provider assesses the environment before takeover, agrees a documented transition plan, secures administrative access, validates backups and cybersecurity, and communicates clearly with the outgoing provider and your employees. Allow enough time for information transfer and avoid changing critical systems during the handover unless a specific risk requires it.
In this guide
THE REASON FOR CHANGE
Why Do Businesses Switch IT Providers?
Most organisations do not consider a change because of one difficult ticket. The decision usually follows a pattern of slow responses, recurring faults, weak communication, limited security guidance or technology that no longer supports the organisation's growth.
Support no longer fits
Response, resolution, ownership or communication no longer meet the needs of employees and operations.
Security gaps remain open
Cybersecurity, backups, identity protection or recovery receive little attention until an incident occurs.
No strategic direction
There is no roadmap, lifecycle plan, budget forecast or regular discussion with business leaders.
If you are still deciding whether the relationship can improve, review The 7 Warning Signs Your Business Has Outgrown Its Current IT Provider and compare the evidence with the current agreement.
PREPARATION
What Should You Do Before Giving Notice?
Read the current contract before agreeing dates with a new provider. Confirm the notice period, renewal date, termination terms, ownership of equipment and licences, data return obligations, and any charges for offboarding or project work.
Clarify internally
Define why the organisation is changing, what good service should look like, who will lead the transition and which dates or business events must be protected.
Clarify contractually
Confirm notice requirements, access and documentation obligations, asset ownership, licence arrangements, data handling and the outgoing provider's handover responsibilities.
For a structured contract review, use What Should You Check Before Renewing Your IT Support Contract?
THE HANDOVER PLAN
The Five-Step IT Provider Transition Framework
A safe transition separates discovery, access, validation and improvement. Each stage should have an owner, target date and clear evidence of completion.
Assess the environment
Review users, Microsoft 365, devices, servers, networks, backups, security controls, applications, licences and suppliers.
Create the plan
Agree milestones, responsibilities, communication, risks, protected business dates and escalation routes.
Secure access
Transfer administrative access through controlled channels and verify that credentials work before takeover.
Validate protection
Check backups, recovery, endpoint security, MFA, administrator accounts, patching and monitoring.
Begin improvement
Move from takeover to proactive support, documentation, risk reduction and a prioritised technology roadmap.
The incoming provider should manage the plan and keep leadership informed. The outgoing provider remains responsible for its contractual duties until the agreed end date.
INFORMATION AND ACCESS
What Information Will Your New IT Provider Need?
The new provider needs enough information to support people, protect systems and manage suppliers from the agreed start date. A missing password is inconvenient; missing ownership or recovery information can create a material business risk.
| Area | Information to collect | Why it matters |
|---|---|---|
| People and access | User list, roles, joiners and leavers, permissions, shared accounts and key contacts. | Support and access decisions need an authorised business owner. |
| Microsoft 365 | Tenant access, licensing, domains, security settings, mail flow and administrator roles. | Email, identity, files and collaboration often depend on the same tenant. |
| Devices and infrastructure | Asset inventory, servers, network equipment, diagrams, warranties and configurations. | The provider must know what exists, where it is and how it is supported. |
| Security and recovery | Endpoint protection, firewall, monitoring, backup, retention, restore tests and incident history. | Existing gaps must be identified before operational responsibility transfers. |
| Applications and suppliers | Business systems, support contacts, contracts, connectivity, telecoms and renewal dates. | Clear boundaries prevent suppliers passing incidents between one another. |
See What Information Should Your New IT Provider Ask for During Onboarding? for a more detailed view of the discovery process.
PROTECT THE BUSINESS
How Do You Maintain Security and Continuity During the Switch?
The handover should reduce uncertainty without making unnecessary changes to live systems. The new provider can first confirm the current state, close urgent risks and schedule broader improvements once control is stable.
Identify decision makers and technical contacts for your business, the outgoing provider and the incoming provider.
Use controlled methods, verify access and avoid sending administrative passwords through ordinary email.
Avoid disruptive work during payroll, financial close, major tenders, events or operational peaks.
Confirm coverage, monitoring, retention and recent restore evidence before relying on the existing setup.
Record administrator accounts, remove obsolete access and reset shared or inherited credentials where appropriate.
Document what was received, tested, changed and still remains outstanding.
COMMON QUESTIONS
Will Switching IT Provider Cause Downtime or Data Loss?
Most provider changes do not require email, files or core systems to be migrated. The new MSP usually takes over management of the existing environment, so employees continue working while access, documentation and monitoring are transferred.
Email and Microsoft 365
The tenant usually stays in place. The incoming provider gains authorised administration and reviews configuration without recreating user mailboxes.
Files and business data
Data should remain in the existing systems. Backups and recovery are validated before changes that could affect availability.
Day-to-day support
Users receive a new contact route and clear start date. Open tickets and known issues should form part of the handover.
Outgoing-provider cooperation
A clear written request, contractual notice and named contacts help keep the process professional and auditable.
Disruption becomes more likely when ownership is unclear, information is requested late or live services are cancelled before dependencies are understood. A documented plan addresses these risks directly.
SELECT THE RIGHT PARTNER
What Should You Look for in a New Managed IT Provider?
Ask each shortlisted provider to explain how it will take responsibility, prove security and maintain continuity. A confident sales presentation is not a substitute for a practical onboarding method.
| Capability | Evidence to request | Why it matters |
|---|---|---|
| Onboarding | A named lead, discovery method, transition plan, milestones and progress reporting. | Shows how the provider will manage the change rather than leaving it to the client. |
| Cybersecurity | Defined controls, alert ownership, risk reporting, incident processes and recovery testing. | Security must continue from the first day of service. |
| Support | Support hours, priorities, response targets, escalation routes and user communication. | Employees need to know how urgent and routine issues will be handled. |
| Microsoft 365 | Identity, device, collaboration, licensing and governance experience. | Most organisations depend on the platform for core daily work. |
| Strategic guidance | Review meetings, roadmaps, lifecycle planning and budget forecasts. | The relationship should improve technology beyond resolving tickets. |
Use How Do You Compare Managed IT Support Providers? to compare scope, capability and evidence consistently.
AFTER THE START DATE
What Happens in the First 30 Days?
The first month should establish control and a reliable baseline. The new provider normally confirms support routes, completes discovery, deploys management tools, validates protection, documents risks and agrees the first improvement priorities.
Stabilise access and support
Verify key administration, publish user contact routes, review urgent tickets and protect critical services.
Complete discovery
Reconcile users, devices, infrastructure, applications, suppliers, licences and documentation.
Validate protection
Review security controls, monitoring, patching, backups, privileged access and recovery evidence.
Set priorities
Present findings, distinguish urgent remediation from planned improvement and agree owners and dates.
Read What Happens in the First 30 Days After Changing IT Provider? for the full onboarding sequence.
PRACTICAL EXAMPLE
A Planned Transition for a 30-Person Glasgow Business
A business operating across several locations wanted to change provider after slow support, recurring issues, poor cost visibility and limited cybersecurity planning. The transition began with a full assessment rather than immediate technical change.
Transition work
Stratiis documented systems and risks, reviewed Microsoft 365 security, verified backup coverage, confirmed access and deployed proactive monitoring.
Business outcome
The organisation moved without planned downtime and gained faster support, clearer costs, improved security visibility and a better basis for long-term planning.
The useful outcome was broader than changing helpdesks. The organisation gained clearer ownership, current documentation and an agreed improvement plan.
IT Provider Transition Checklist
Use this checklist to confirm that the key dependencies have an identified owner before the current service ends.
Tenant, domains, licences, administrator roles and security configuration.
Registrar ownership, renewal details, DNS access and authorised contacts.
Firewall, switches, Wi-Fi, internet circuits, support details and configurations.
Coverage, destinations, retention, monitoring, credentials and restore evidence.
Current user list, permissions, assigned equipment, security status and lifecycle.
Business systems, licences, contracts, renewal dates and escalation contacts.
Outstanding tickets, known problems, planned projects and unresolved risks.
Start date, contact channels, escalation route and instructions for employees.
FREQUENTLY ASKED QUESTIONS
Questions About Changing IT Provider
How long does it take to switch IT providers?
A straightforward transition may take a few weeks. Timing depends on the notice period, the quality of existing documentation, the number of users and sites, and any urgent security or access issues.
Should we tell the current provider before choosing a replacement?
Review the agreement and select a suitable transition approach first. The formal notice should follow the contract and give both providers enough time to coordinate.
Will employees need new email accounts?
Usually no. The organisation normally keeps its Microsoft 365 tenant and email addresses while the incoming provider takes over administration.
What if documentation is incomplete?
The new provider can discover and document the environment, but missing access or ownership may extend the transition. Identify these gaps early and track them as risks.
Can the old provider refuse to hand over passwords?
Access and ownership depend on the contract and the systems involved. A documented, authorised handover request and clear escalation route help resolve gaps professionally.
When should security changes begin?
Urgent risks should be addressed promptly. Wider changes should follow a controlled plan once access, backups and business dependencies are understood.
PLAN WITH CONFIDENCE
How Should You Start the Switching Process?
Start by defining the business requirement, reviewing the current agreement and identifying critical services and dates. Ask the proposed provider to explain its onboarding process, responsibilities, evidence and communication before you commit.
Review the position
Record service issues, risks, contract dates, current suppliers and the outcomes leadership expects.
Select with evidence
Compare service scope, cybersecurity, onboarding, reporting, strategy and total cost.
Agree the handover
Set owners, dates, information requirements, communication and completion criteria before notice expires.
Planning a Change of IT Provider?
Stratiis can review your current position, plan a secure handover and coordinate the move to managed IT support with minimal disruption to employees and operations.